TL;DR: We published a post-mortem on October's PHP and Node.js security response — what went well, what didn't, and what we're changing. We also shipped smarter database reads for the framework, added a Resend integration into Cloud, and PHP version checks in Forge.
The Laravel framework added QUERY routes, protection against stale reads after database writes, and single-server scheduling defaults.
Laravel Cloud added a Resend integration for transactional email, a Cloud scheduler for apps in any language Cloud supports, and domain health checks for DNS and SSL issues.
Laravel Forge added PHP security advisories and clearer handling for failed server provisioning.
Laravel Framework
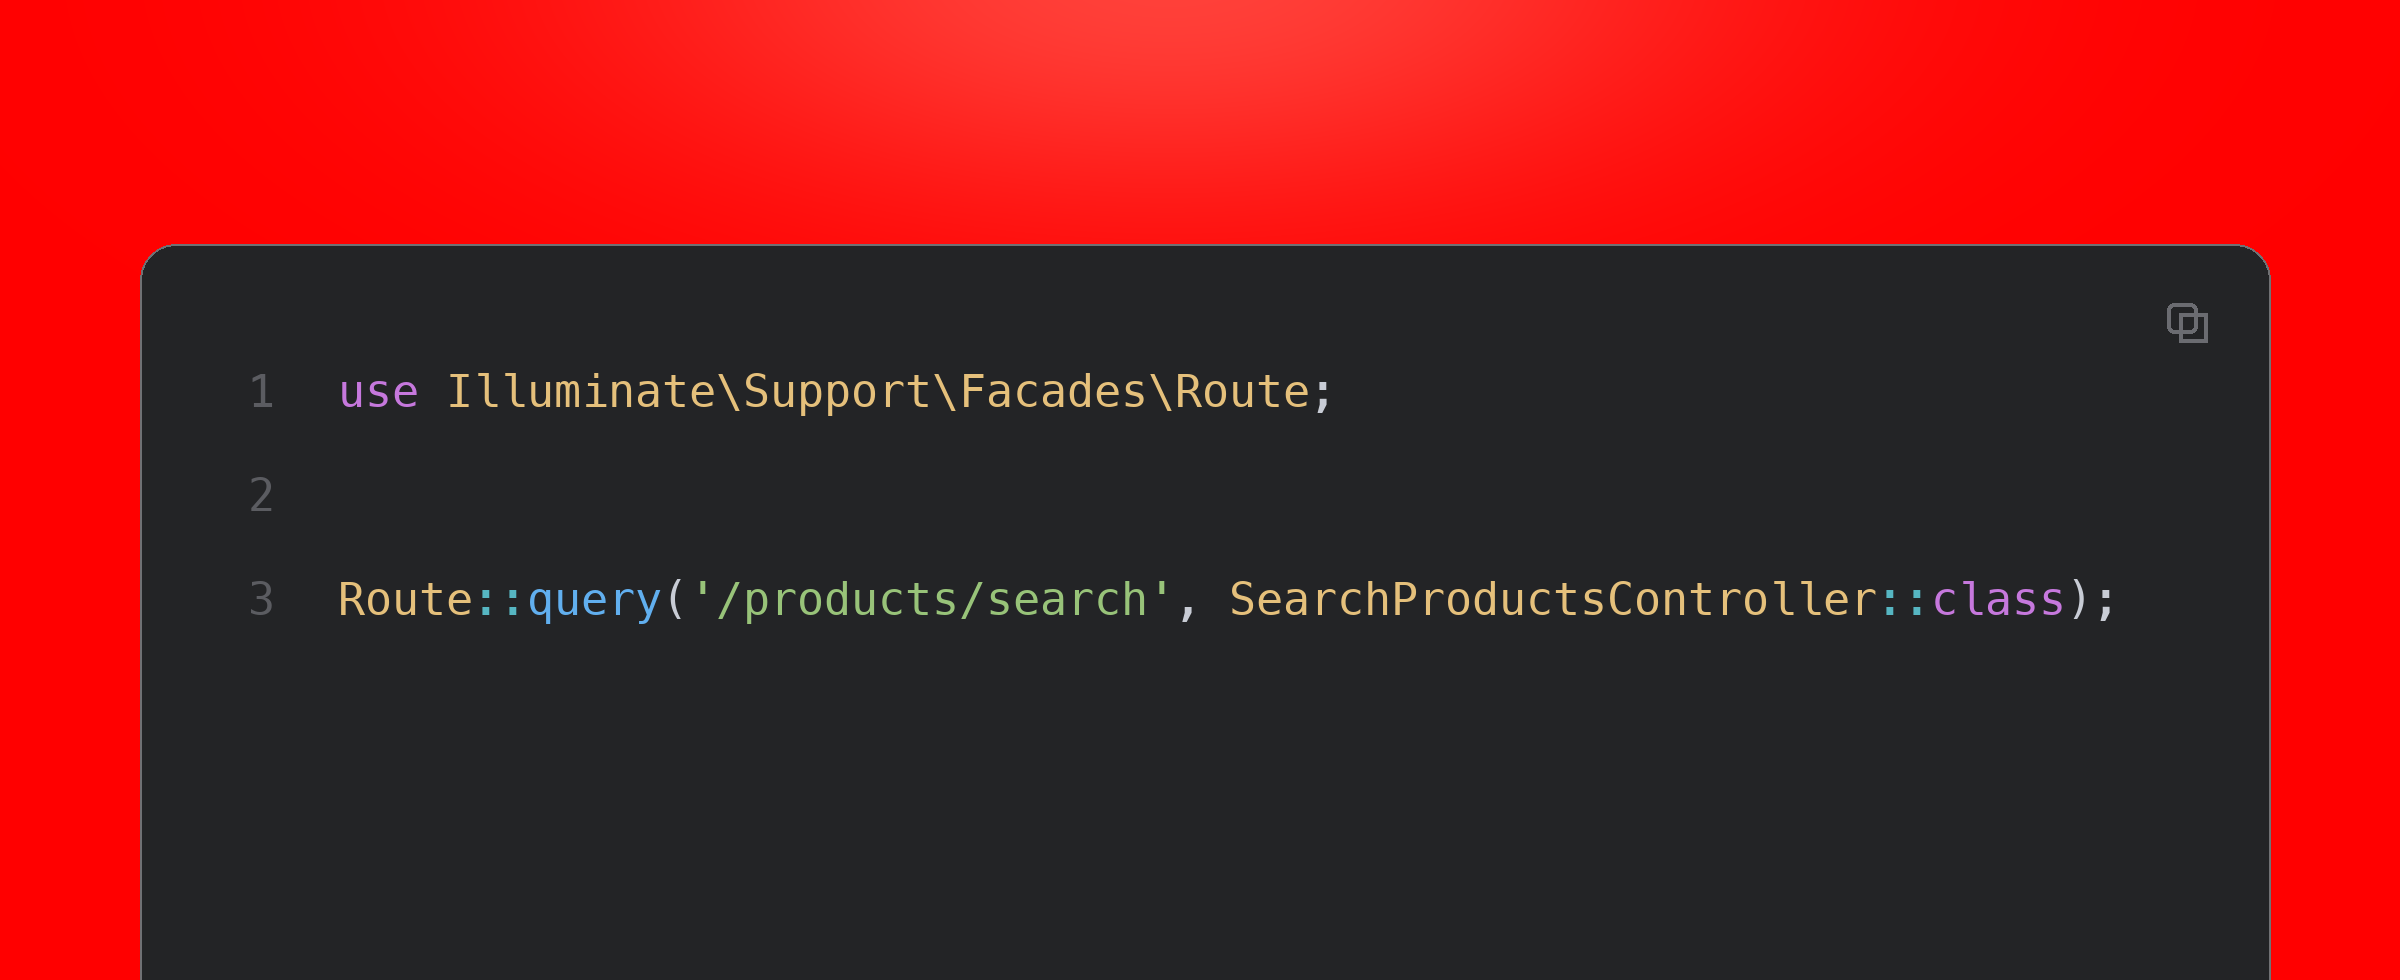
Register QUERY Routes: Laravel now supports the
HTTP QUERYmethod in routing, includingRoute::query().Route::any()also matchesQUERYrequests. UnlikeGET,QUERYrequests can carry a body, so these routes stay subject to CSRF verification in thewebmiddleware group.Avoid Stale Reads After Database Writes: The opt-in
PreventStaleDatabaseReadsmiddleware routes a user's reads to the write connection for a couple of seconds after that user writes, so they don't immediately hit a replica that hasn't caught up yet. Pair it with the newConnection::usingWritePdo()for one-off reads that need the same guarantee.Run Scheduled Tasks on One Server by Default:
Schedule::alwaysOnOneServer()opts every eligible scheduled task intoonOneServer()at once, so multi-server deployments don't silently double up on scheduled jobs.Assert Fake Dispatches by Their Properties: Queue, bus, event, and notification fakes now accept an array of expected properties in their assertions, so tests can match a dispatched object's attributes without writing a callback.
Read the full Laravel Framework changelog.
Laravel Cloud
Resend integration: Connect a Resend account to your organization once, and Cloud imports your sending domains, shows you the DNS records to add, and tracks verification status. Attach email to an environment like any other resource—Cloud mints the API key and injects
RESEND_API_KEY,MAIL_MAILER,MAIL_FROM_ADDRESS, andMAIL_FROM_NAMEfor you.Cloud scheduler: Any language Cloud supports can now run commands on a schedule without installing cron or running a scheduling process. Use a preset (hourly, daily, weekly, monthly) or a custom cron expression; Cloud validates it and describes it in plain language as you type. Each run's output, exit code, and timing show up in the Logs dashboard.
Domain health checks: Cloud now checks every connected domain hourly to confirm its DNS record still points to Cloud and that its SSL certificate is renewing. If something breaks, your team gets flagged on the environment canvas and notified by email or Slack before visitors notice.
Read the full Laravel Cloud changelog.
Laravel Forge
PHP security advisories: Forge now flags PHP versions affected by the October 2026 PHP security release across your servers, with guidance on whether a patched version is available. A new Recheck versions button syncs Forge with what's actually installed.
Provisioning failure handling: Servers that can't finish provisioning are now marked failed, with an alert, next-step guidance, and a delete action, instead of sitting in limbo. Forge also retries PHP and Nginx installs before giving up.
Read the full Forge changelog.